Tag Archives: sas

Welcome to SAS City 2025!

Hi folks!

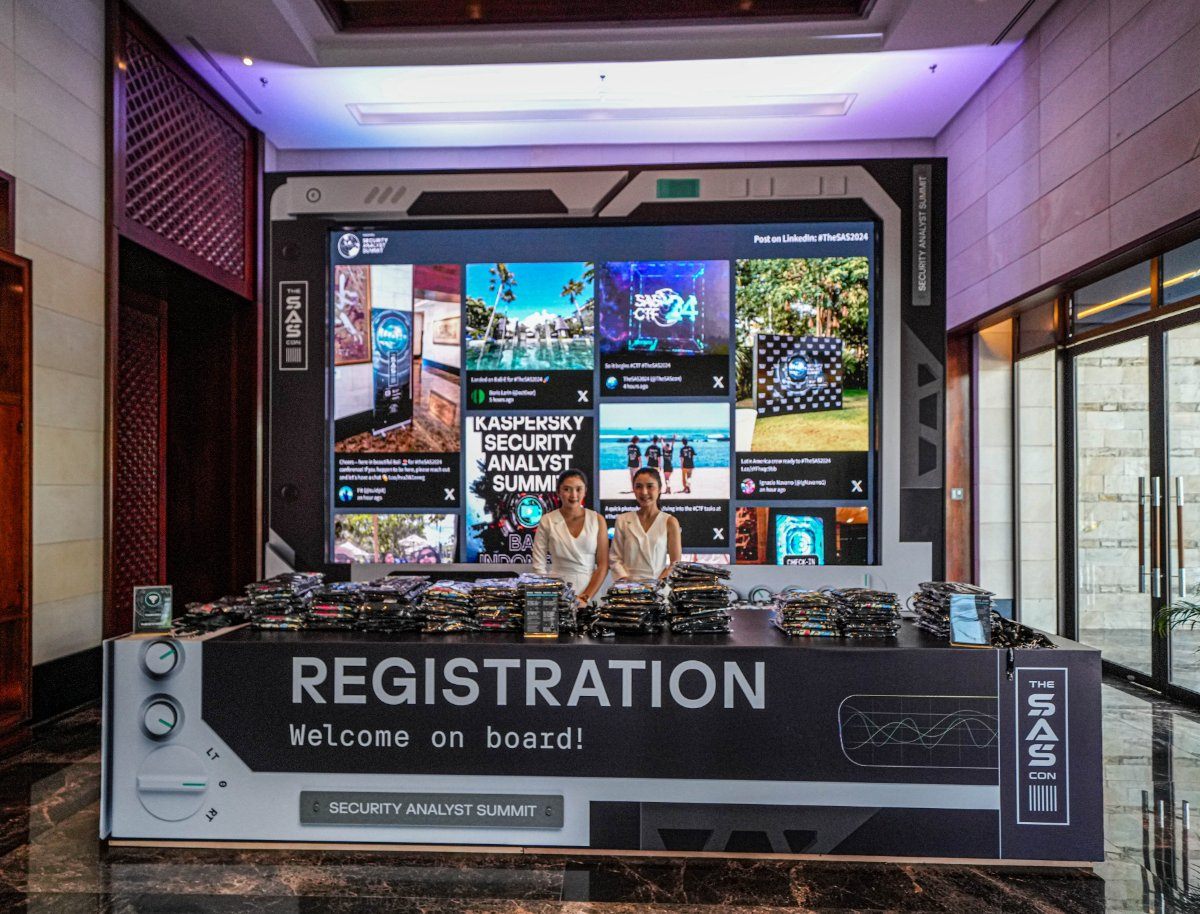
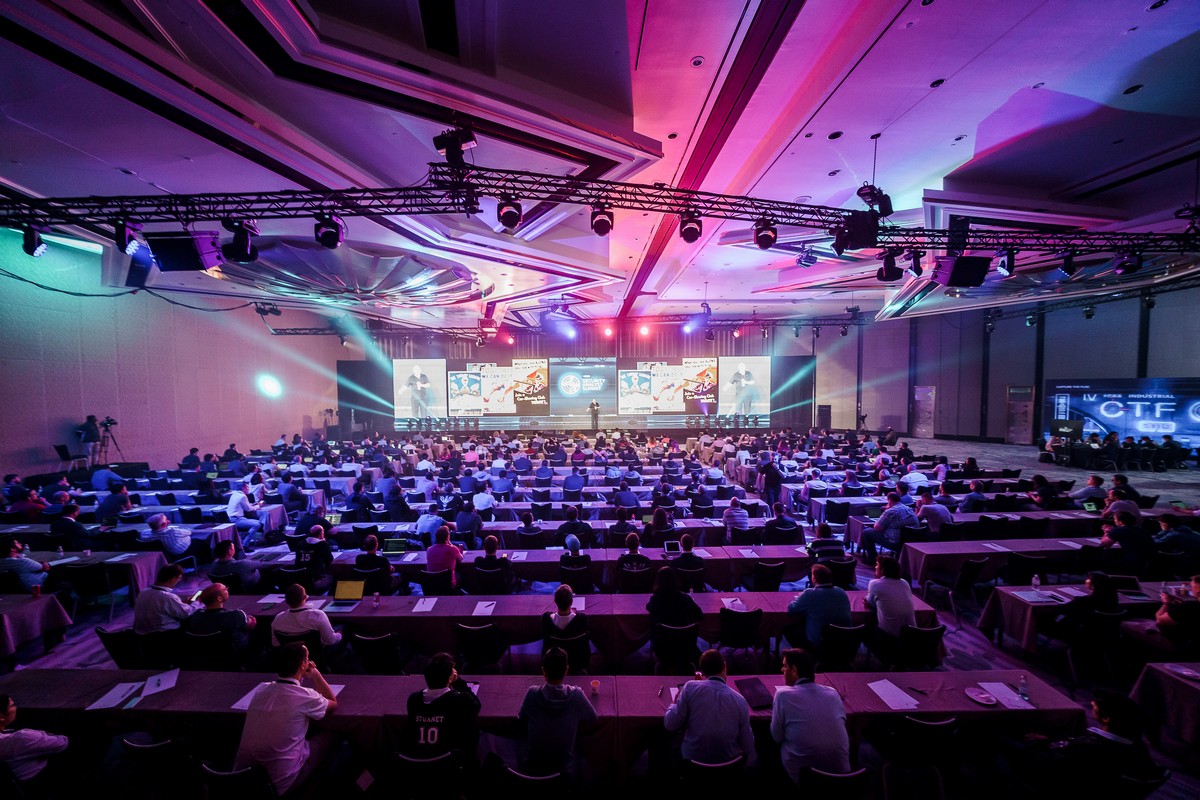
Phew! Another year – and another Security Analyst Summit wrapped. This time is was – ooh, let me see: yes, the 16th edition of the event, and it was held in the Thai resort village of Khao Lak (here) – about a hundred kilometers north of Phuket.

In case you don’t know already, SAS is a one-of-a-kind security conference – very different from the usual, more buttoned-up, corporate events in the field. It actually started out as a gathering for our internal team – back when our own group of experts was growing and becoming more global. As it did, it made perfect sense to bring everyone together in person once a year: so the team members could get acquainted, interact face-to-face, and share their impressive research and investigations with each other. And it turned out to be a brilliant idea.

Eventually, someone (clearly thinking ahead) suggested we should invite outside cybersecurity experts, and so we began to welcome colleagues from other companies and organizations too. And slowly but surely, year after year, SAS grew into what it is now – a global conference for top analysts that still manages to maintain a bit of a party spirit. Here we allow ourselves to bend the rules a little, play, break from tradition, and do things our own way. But more than that, SAS has kept its club-like, invite-only character: a special expert committee decides who gets to attend. This has helped preserve its more open, candid atmosphere, where folks feel comfortable sharing more than they would at a typical IT security event.

Read on…

SAS-2024 – truly cosmic (and world-record breaking!)

Hai folks!

The official part of our SAS-2024 conference: done.

Now – the fun part: our esteemed delegates, respected speakers, honorable guests (and I!) continue to enjoy this picture-perfect corner of the island of Bali while they come to their senses – still digesting the mega-doses of first-class cybersecurity content they’ve just received…

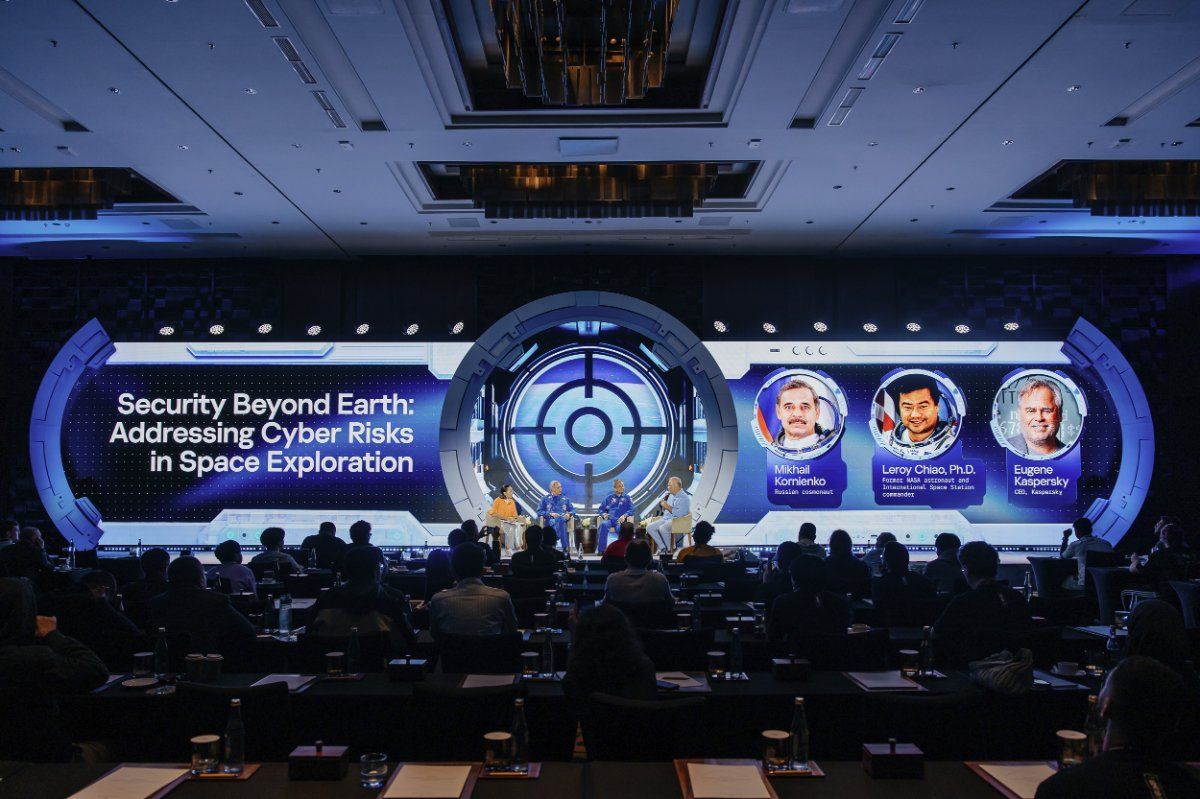
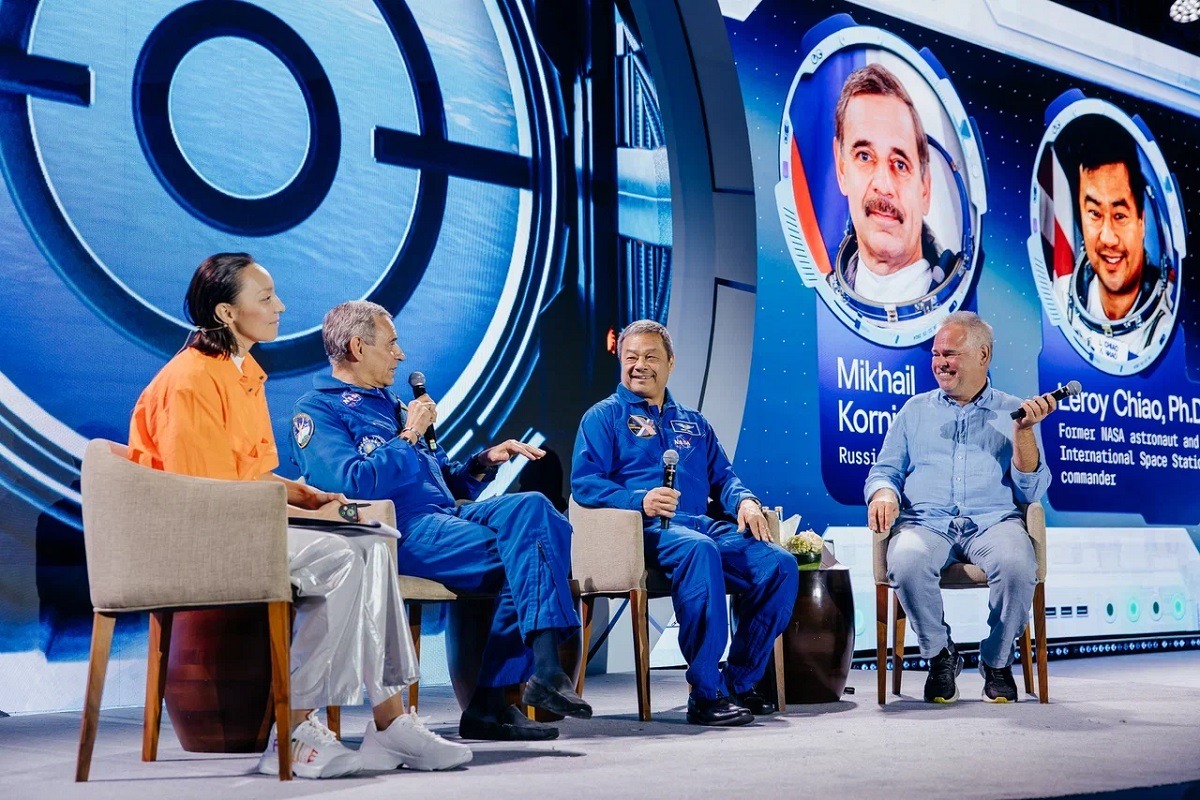
As to my (direct) participation in the proceedings (besides watching the speeches), the highlight for sure was my being on stage – not as interviewee, but as interviewer. I can’t recall if I’d ever done such a thing before (if I had it was decades ago). Anyway, it felt like the first time – and early on I was really nervous! Yes – me! But I soon got into the swing of it – no doubt partly due to just how interesting my interviewees were: the Russian cosmonaut Mikhail Kornienko and American astronaut Leroy Chiao! We discussed all sorts of cybersecurity issues in space: how they duplicate the comms channels on the International Space Station, who’s responsible for installing updates, what happens if an incident occurs, and lots more besides…

Read on…

SAS-2024 – what you waiting for?!

Hi folks – from Indonesia, where we’re holding our yearly international cybersecurity conference SAS – the Security Analyst Summit.

Dozens of cybersecurity events take place around the world every year, but ours has its own special format – its own special work-hard-play-hard ethic, and it’s always by the sea in a tropical clime. It attracts leading analysts and researchers of the most complex cyberattacks, and this year we’re in Bali ->

Read on…

Infosec top-brass: back again – in person – at SAS!

Trumpets, drum roll, applause, cheering, whistling! Herewith, two bits of news for you: one good, the other – even better!…

First: this year we’ll be having our 15th annual cybersecurity conference – the Security Analyst Summit (SAS). Fifteen? Oh my gone-where-has-the-time?!

Second: We’re finally back to an offline, aka – in-person, aka – face-to-face format, just like old times!

// In recent years this conference and indeed many others have been online.

Our tradition of annually bringing together top cybersecurity experts, academics and business folks from all around the world in a warm and pleasant location began way back in 2009. (Blimey – 2009 seems like yesterday; it’s a full 14 years ago!) Back then it was a lot smaller in size, but over the years it’s grown gradually to become one of the key yearly fixtures on the global cybersecurity-event calendar.

// For those who might want to review how SAS has developed over the years, check this tag out.

This year the warm and pleasant location will be Phuket in Thailand, where the conference will run from October 25 to 27. As usual we’ll be presenting, sharing and discussing the latest trends in cybersecurity (including recently uncovered APT attacks) plus cutting-edge achievements in the field of research and technology.

Spoiler: emphasis will be placed on the following topics:

  • Protection of industrial infrastructure;
  • ICS/OT security;
  • Supply-chain and IoT attacks;
  • Methods for tackling ransomware and the darknet;
  • The unveiling of our new training course in reverse engineering and Ghidra – presented by our GReAT.

And we’ve already announced the call for papers! If you want to present your ground-breaking research or innovational solution, enter the respective info on the site…

So there you have it folks – SAS 2023: approaching fast. It’s going to be GReAT, it’s going to be interesting, it’s going to be super-informative, it’s going to be a super-success – as always!…

See you in Phuket!…

In closing – a quick SAS photo-retrospective…

Security analysts of the world – united (remotely)!

The world seems to be slowly opening back up – at least a little, at least in some places. Some countries are even opening up their borders. Who’d have thought it?

Of course, some sectors will open up slower than others, like large-scale events, concerts and conferences (offline ones – where folks turn up to a hotel/conference center). Regarding the latter, our conferences too have been affected by the virus from hell. These have gone from offline to online, and that includes our mega project the Security Analyst Summit (SAS).

This year’s SAS should have taken place this April in one of our favorite (for other K-events) host cities, Barcelona. Every year – apart from this one – it takes place somewhere cool (actually, normally quite hot:); for example, it was in Singapore in 2019, and Cancun, Mexico, in 2018. We’d never put on a SAS in Barcelona though, as we thought it might not be ‘fun’ or ‘exotic’ enough. But given that folks just kept on suggesting the Catalonian city as a venue, well, we finally gave in. Bit today, in May, we still haven’t had a SAS in Barcelona, as of course the offline, planned one there had to be postponed. But in its place we still had our April SAS – only on everyone’s sofa at home online! Extraordinary measures for extraordinary times. Extraordinarily great the event turned out to be too!
But we’re still planning on putting on the offline SAS in Barcelona – only later on, covid permitting. But I’m forever the optimist: I’m sure it will go ahead as planned.

It turns out there are quite few upsides to having a conference online. You don’t have to fly anywhere, and you can view the proceedings all while… in bed if you really want to! The time saved and money saved are really quite significant. I myself watched everything from a quiet corner of the flat (after donning my event t-shirt to get into SAS mode!). There were skeptics, however: an important element of any conference – especially such a friendly, anti-format one like SAS – is the live, human, face-to-face interaction, which will never be replaced by video conferencing.

I was really impressed with how things went. Kicking it off we had more than 3000 folks registered, out of which more than a thousand were actually watching it any one time over the three days – peaking sometimes above 2000. Of course most would have picked and chosen their segments to watch instead of watching it non-stop. The newly introduced training sessions, too, were well attended: around 700 for all of them – a good indicator folks found them interesting.

And for SAS@Home a special program had been prepared – and all in just two weeks! Why? Well, the heart of our conference is hardboiled, hardcore geekfest techy stuff: very detailed investigations and reports from the world’s top cybersecurity experts. But for SAS@Home the audience was to be bigger in number, and broader in audience profile – not just tech-heads; so we experimented – we placed an emphasis on a learning program, not in place of the detailed investigations and reports, but in addition to them.

And we seemed to have gotten the balance just right. There was the story of the Android Trojan PhantomLance in Google Play, which for several years attacked Vietnamese Android users. There were presentations on network security and zero-day vulnerabilities. On the second day there was the extraordinarily curious talk by our GReAT boss, Costin Raiu, about YARA rules, with a mini-investigation about chess as a bonus!
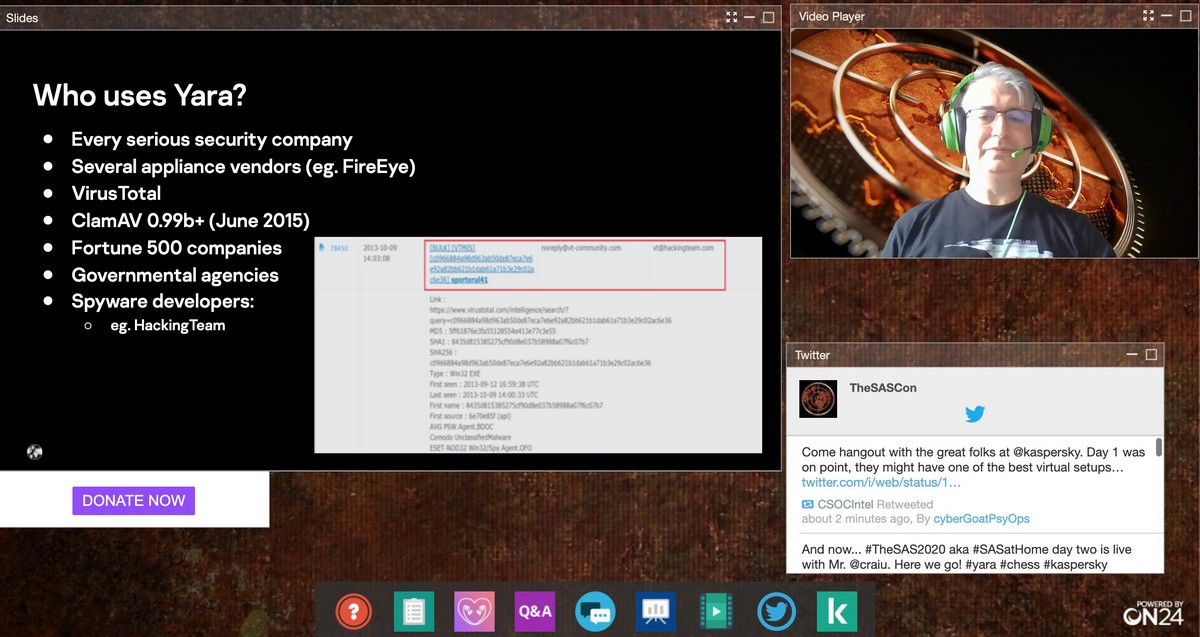
After that there was Denis Makrushkin on bug-hunting and web applications. And on the third day things got really unusual. It’s not every cybersecurity conference where you can hear about nuances of body language; or where – straight after that comes selecting methods of statistical binary analysis! But at SAS – par for the course ).

As per tradition, a huge thanks to everyone who helped put on the show: all the speakers, the organizers, the partners from SecurityWeek, the viewers, the online chatters, and the tweeters. And let’s not forget the flashmob we launched during SAS – quarantunities – dedicated to what folks have been getting up to during lockdown at home, including someone starting to cook every day, someone learning French, and someone else switching from life in the metropolis to that in the countryside.

In all, a great success. Unexpected format, but one that worked, and then some. Now, you’ll no doubt be tiring a little of all the positivity-talk of late about using the crisis and lockdown to one’s advantage. Thing is, in this instance, I can’t do anything but be positive, as it went so unbelievably well! Another thing: ‘We’ve had a meeting, and I’ve decided’ (!) that this online format is here to stay – even after covid!

Finally, one last bit of positivism (really – the last one, honest :). As our experts David Jacoby and Maria Namestnikova both pointed out during the final session, there are other positive things that have come out of quarantining at home: more folks are finding the time to stay fit with home exercise routines; there’s an emphasis being put on physical health generally (less rushing about and grabbing sandwiches and takeaways, etc.); folks are helping each other more; and levels of creativity are on the rise. Indeed, I’ve noticed all those things myself too. Nice. Positive. Eek ).

That’s all from me for today folks. And that’s all from SAS until we finally get to sunny Barcelona. Oh, and don’t forget…: another one for your diary for next year: SAS@home-2021!

PS: Make sure to subscribe – and click the bell for notifications!! – to our YouTube channel: we’ll be putting up there recordings of all sessions gradually. Yesterday the first one was published!…

Security Analyst Summit – start watching tonight – from your sofa!

As many of you will know, every year we organize the mega security conference called Security Analyst Summit in an interesting (at least sunny, often sandy) location. The event is something different for the industry – never dull, never boring, never format-following. We bring together big-name speakers and guests in an exclusive invite-only format to discuss the very latest – loudest – cybersecurity news, investigations, stories, curiosities and so on. No politics! Only professional discussion of cybersecurity – but lightly, relaxed, friendly… awesomely! And we do it so well SAS is becoming one of the most important conferences in the industry. By way of example, here’s my write-up on last year’s event – in Singapore.

Now, this year’s event – our 12th! – should have opened today, April 28, in sunny Barcelona. But of course – for obvious reasons, that’s just not happening (.

However, we felt that to cancel SAS would be giving in; we couldn’t just drop it this year: how would world cybersecurity cope?! Accordingly, we decided to premiere this year’s SAS online; and not only that but… – for free (!), and for everyone and anyone who wants a taste! Soooo – here’s introducing: SAS@Home, and it’s starting later today (11am Eastern; 8am PST, 4pm London, 6pm Moscow), so hurry up and register! More than a thousand folks have already registered, so it looks like the new format isn’t putting people off. We’ll just have to see how this first online SAS goes; maybe in the future we’ll have two running parallel – online and offline!

Here’s a quick overview of the schedule:

Read on…

Hi Cancun – for the last time!

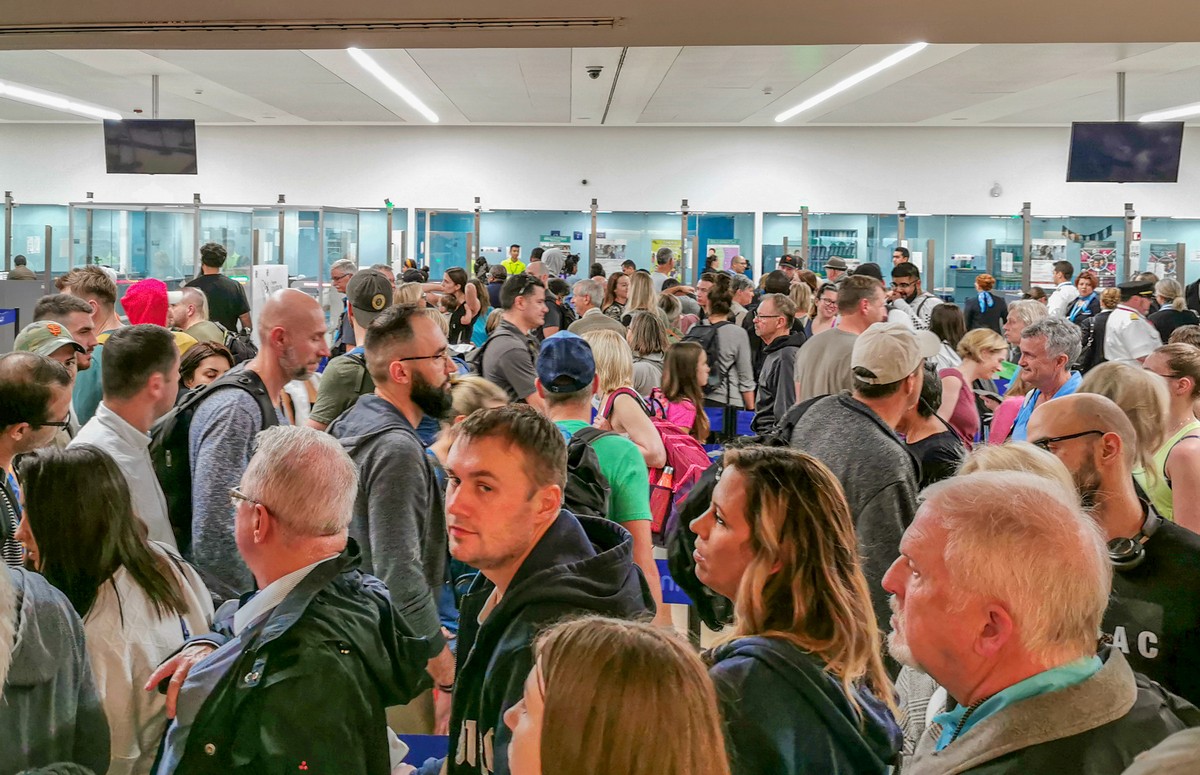
“Buenos tardes!” said the hospitable Yucatán native. And then, smilingly, ushered us toward a particular line for passport control – which took a full 90 minutes for us to get to the front of!

“Buenos noches!”, we answered, while muttering other phrases under our breath I shouldn’t repeat here. But it got worse: out of a full 30+ passport control windows only six (6!) were working! And it was clear the border control staff wasn’t in any way speeding up its work given this avia-logisitical collapse. But then, it turned out, upon our asking if this was indeed a one-off collapse, that this happens all the time: several flights arrive around the same time all the time. So, like, they’re fully aware of the problem, but do nothing about it! I mean, they should be happy for all the dollars all these (many!) tourists arriving in Mexico every day will be spending, but they treat them with contempt! At one point I thought there could be some kind of revolt and lynchings; indeed a fight did break out in the next line to us (I think with tourists from Canada): someone got punched in the face for jumping the line!

Actually, we love(d) Cancun: since 2011 we’ve put on a full 12 (!) business events here – including the one I’m about to tell you about! Good infrastructure, safe, ocean, beaches, sun, tequila, and venues able to handle 500+ guests for large conferences (like our Security Analyst Summit (SAS), which, incidentally, took place here a full three times, in 2012, 2015 and 2018). And what else do we ask of a destination for our bashes? For all our guests to NEVER have to wait in lines at the airport for hours after a long flight. But this clearly is unattainable. Therefore, accordingly, this is the LAST event of ours in Cancun. Buenos huegos. No, better…: Buenos &!#*%!!

The basic ingredients for the format were present, as per: first work hard – then play hard! But the world is changing, audiences are changing too, and then there are all the geopolitical cataclysms that come in waves – which we sometimes even try to surf ). Accordingly, we made a few changes to the basic format.

Read on

Cyber-news from the dark side – ver. SAS-2019.

Hi folks!

Herewith, the next in my series of occasional iNews, aka cyber-news from the dark side updates – this one based on some of the presentations I saw at our annual Security Analyst Summit in Singapore last month.

One of the main features of every SAS is the presentations given by experts. Unlike other geopolitically-correct conferences, here the analysts up on stage share what they’ve discovered regarding any cyberthreat, no matter where it may come from, and they do this based on principle. After all, malware is malware and users need to be protected from all of it, regardless of the declared virtue of the intentions of those behind it. Just remember the boomerang effect.

And if certain media outlets blatantly lie about us in response to this principled position, so be it. And it’s not just our principles they attack – for we practice what we preach: we’re way ahead of the competition when it comes to the numbers of solved cyberespionage operations. And we’re not planning on changing our position in any way to the detriment of our users.

So here are a few synopses of the coolest investigations talked about at SAS by the experts behind them. The most interesting, most shocking, most scary, most OMG…

1. TajMahal

Last year, we uncovered an attack on a diplomatic organization from Central Asia. Of course, that an organization like that is interesting to cybercriminals should come as no surprise. The information systems of embassies, consulates and diplomatic missions have always been of interest to other states and their spy agencies or generally any bad guys with sufficient technical ability and financial wherewithal. Yes, we’ve all read spy novels. But here was something new: here a true ‘TajMahal’ was built for the attacks – an APT platform with a vast number of plugins used (we’ve never seen so many used on one APT platform – by far) for all sorts of attack scenarios using various tools.

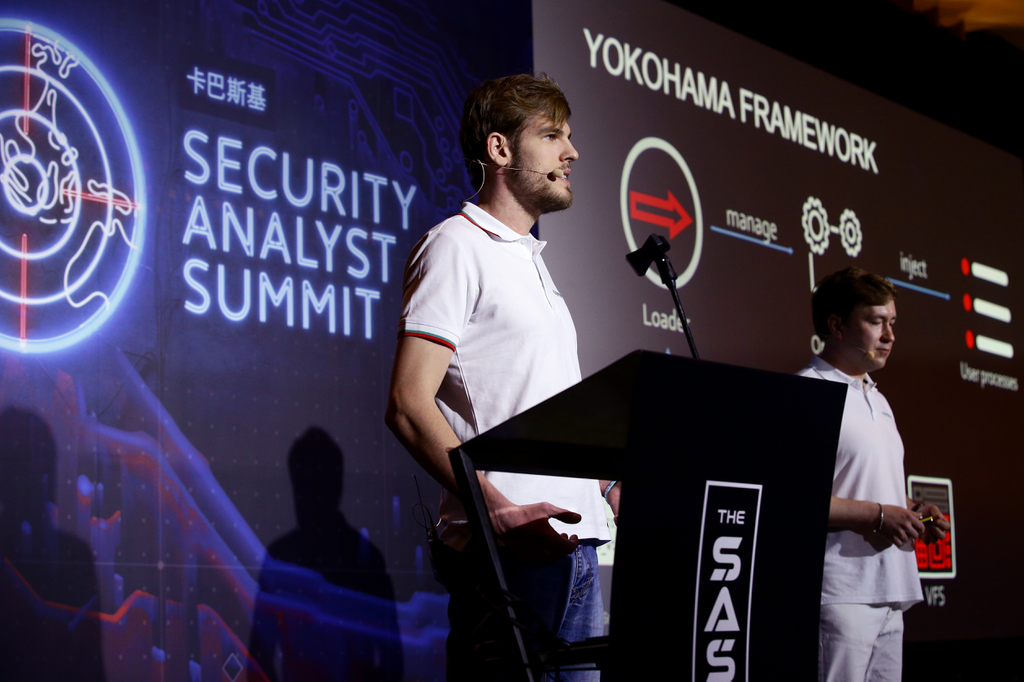
The platform consists of two parts: Tokyo and Yokohama. The former is the main backdoor, which also fulfils the function of delivery of the latter malicious program. The latter has very broad functionality: stealing cookies, intercepting documents from the printer queue, recording VoIP calls (including WhatsApp and FaceTime), taking screenshots, and much more. The TajMahal operation has been active now for at least five years. And its complexity would suggest that it’s been built with more than one target in mind; the rest remain for us to find…

Details of this APT-behemoth you can find here.

Read on…